Look beyond the tool name.
The account, the device and the way a tool is used all matter. My aim is to bring that context together so an observation becomes something people can act on.
My vision for Nyxus is practical: give organisations the context to decide how AI belongs in their work, while keeping control of their own data.
“Knowing a tool is installed is a starting point. I want the platform to help people understand the use behind it, and decide what happens next.”
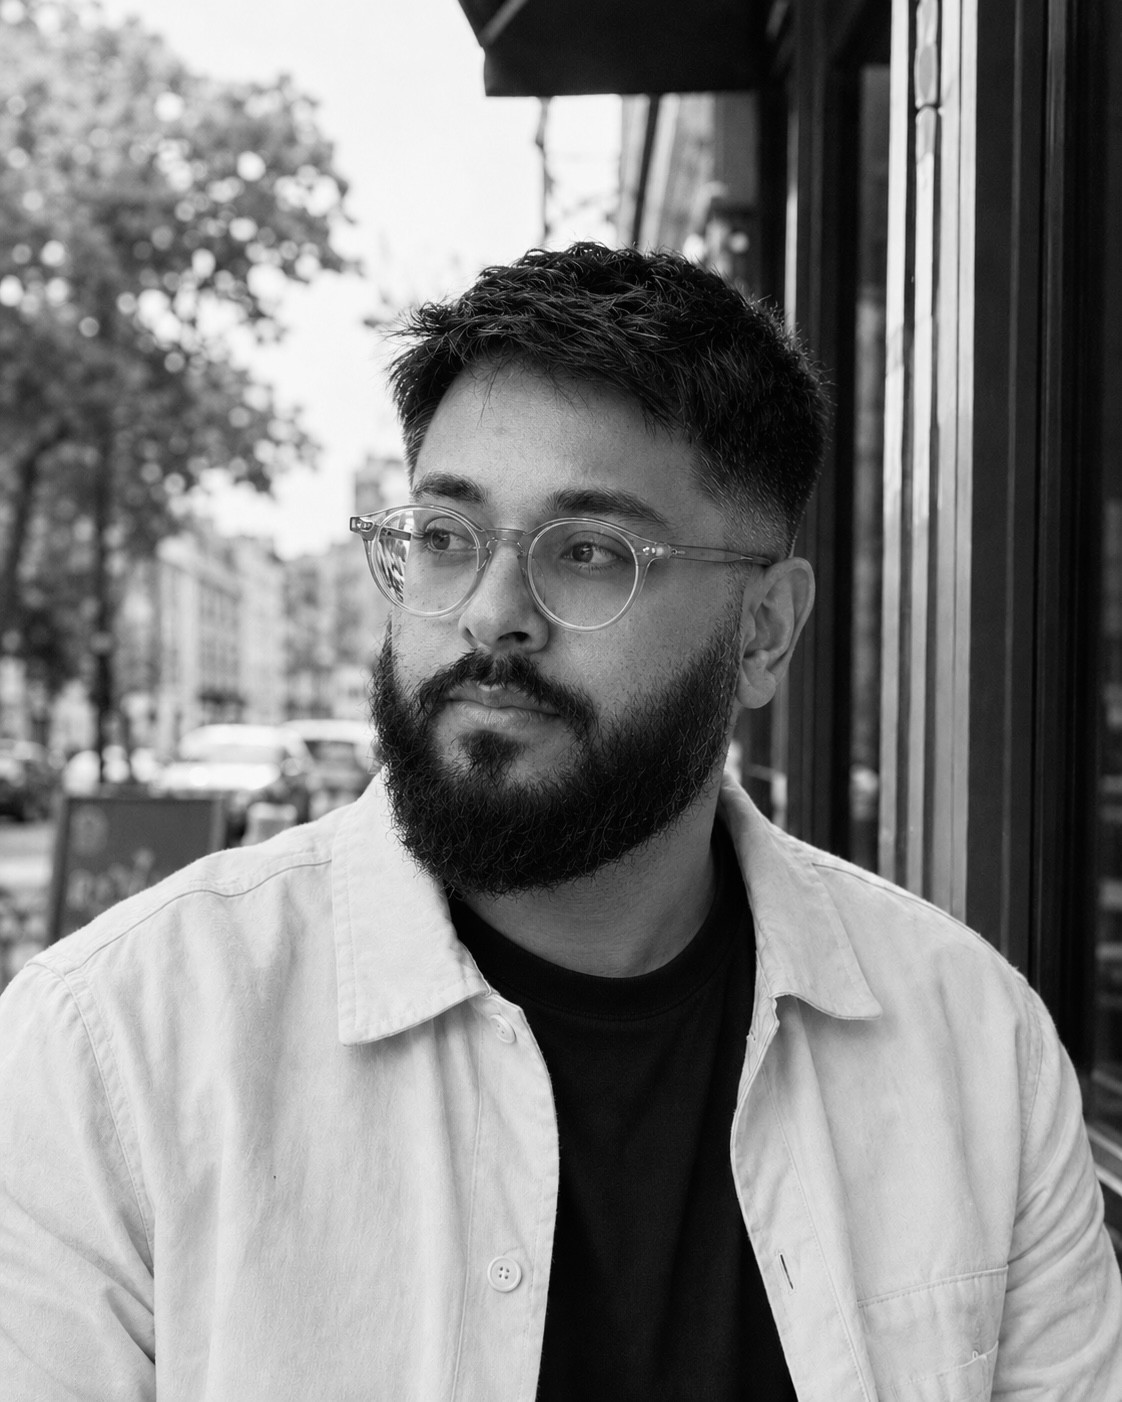 Aman KarirCreator, Shadow AI Guard & Nyxus
The account, the device and the way a tool is used all matter. My aim is to bring that context together so an observation becomes something people can act on.
Governance needs an owner, a reason and a way to review a decision. The platform should support that judgement and make it easier to follow through.
Self-hosting is central to the approach. Organisations should be able to investigate their AI use within infrastructure they control.
My direction for Nyxus is a practical enterprise workspace: a place to understand findings, record decisions and return to them as circumstances change.
What AI is actually running at work? I started with a weekly script to answer that question. It grew into Shadow AI Guard, and then into the foundation for Nyxus. The scope has grown; the reason for building it remains the same.
I started with a Python script that checked our existing tools for known AI services and printed a report.
It worked, but only when I ran it. By the time I read the results, things had often moved on.
I moved the scanners onto our Kubernetes cluster and scheduled them to run automatically. Findings went into Grafana, with warnings sent to Slack.
Then I added a browser extension and endpoint collector to see which accounts people were using across browser, CLI, IDE and desktop AI tools.
Our Linux machines sat outside MDM, leaving a gap. I brought them into scope through our RMM tools and other routes that didn’t depend on MDM.
I wanted to do more than spot AI use. I added Paste Guard and browser AI security, with their findings going into the same place as everything else.
Grafana helped me see what was happening. I still needed somewhere to follow it up.
Shadow AI Guard brought the findings into one console, with a place to review them and decide what to do.
Next, I packaged Shadow AI Guard so other teams could run it too. The managed version supports Docker Compose and Kubernetes, with one command to get started.
Nyxus builds on that foundation as an enterprise workspace. It’s the next stage of the same idea: understand what’s being used, then decide what happens next.
It’s coming soon.
Shadow AI Guard is open source; Nyxus is being built privately alongside it. This is both repositories together, a day at a time, and every week since the first commit has some.